Home-Based EDR System
Prototype · 2026
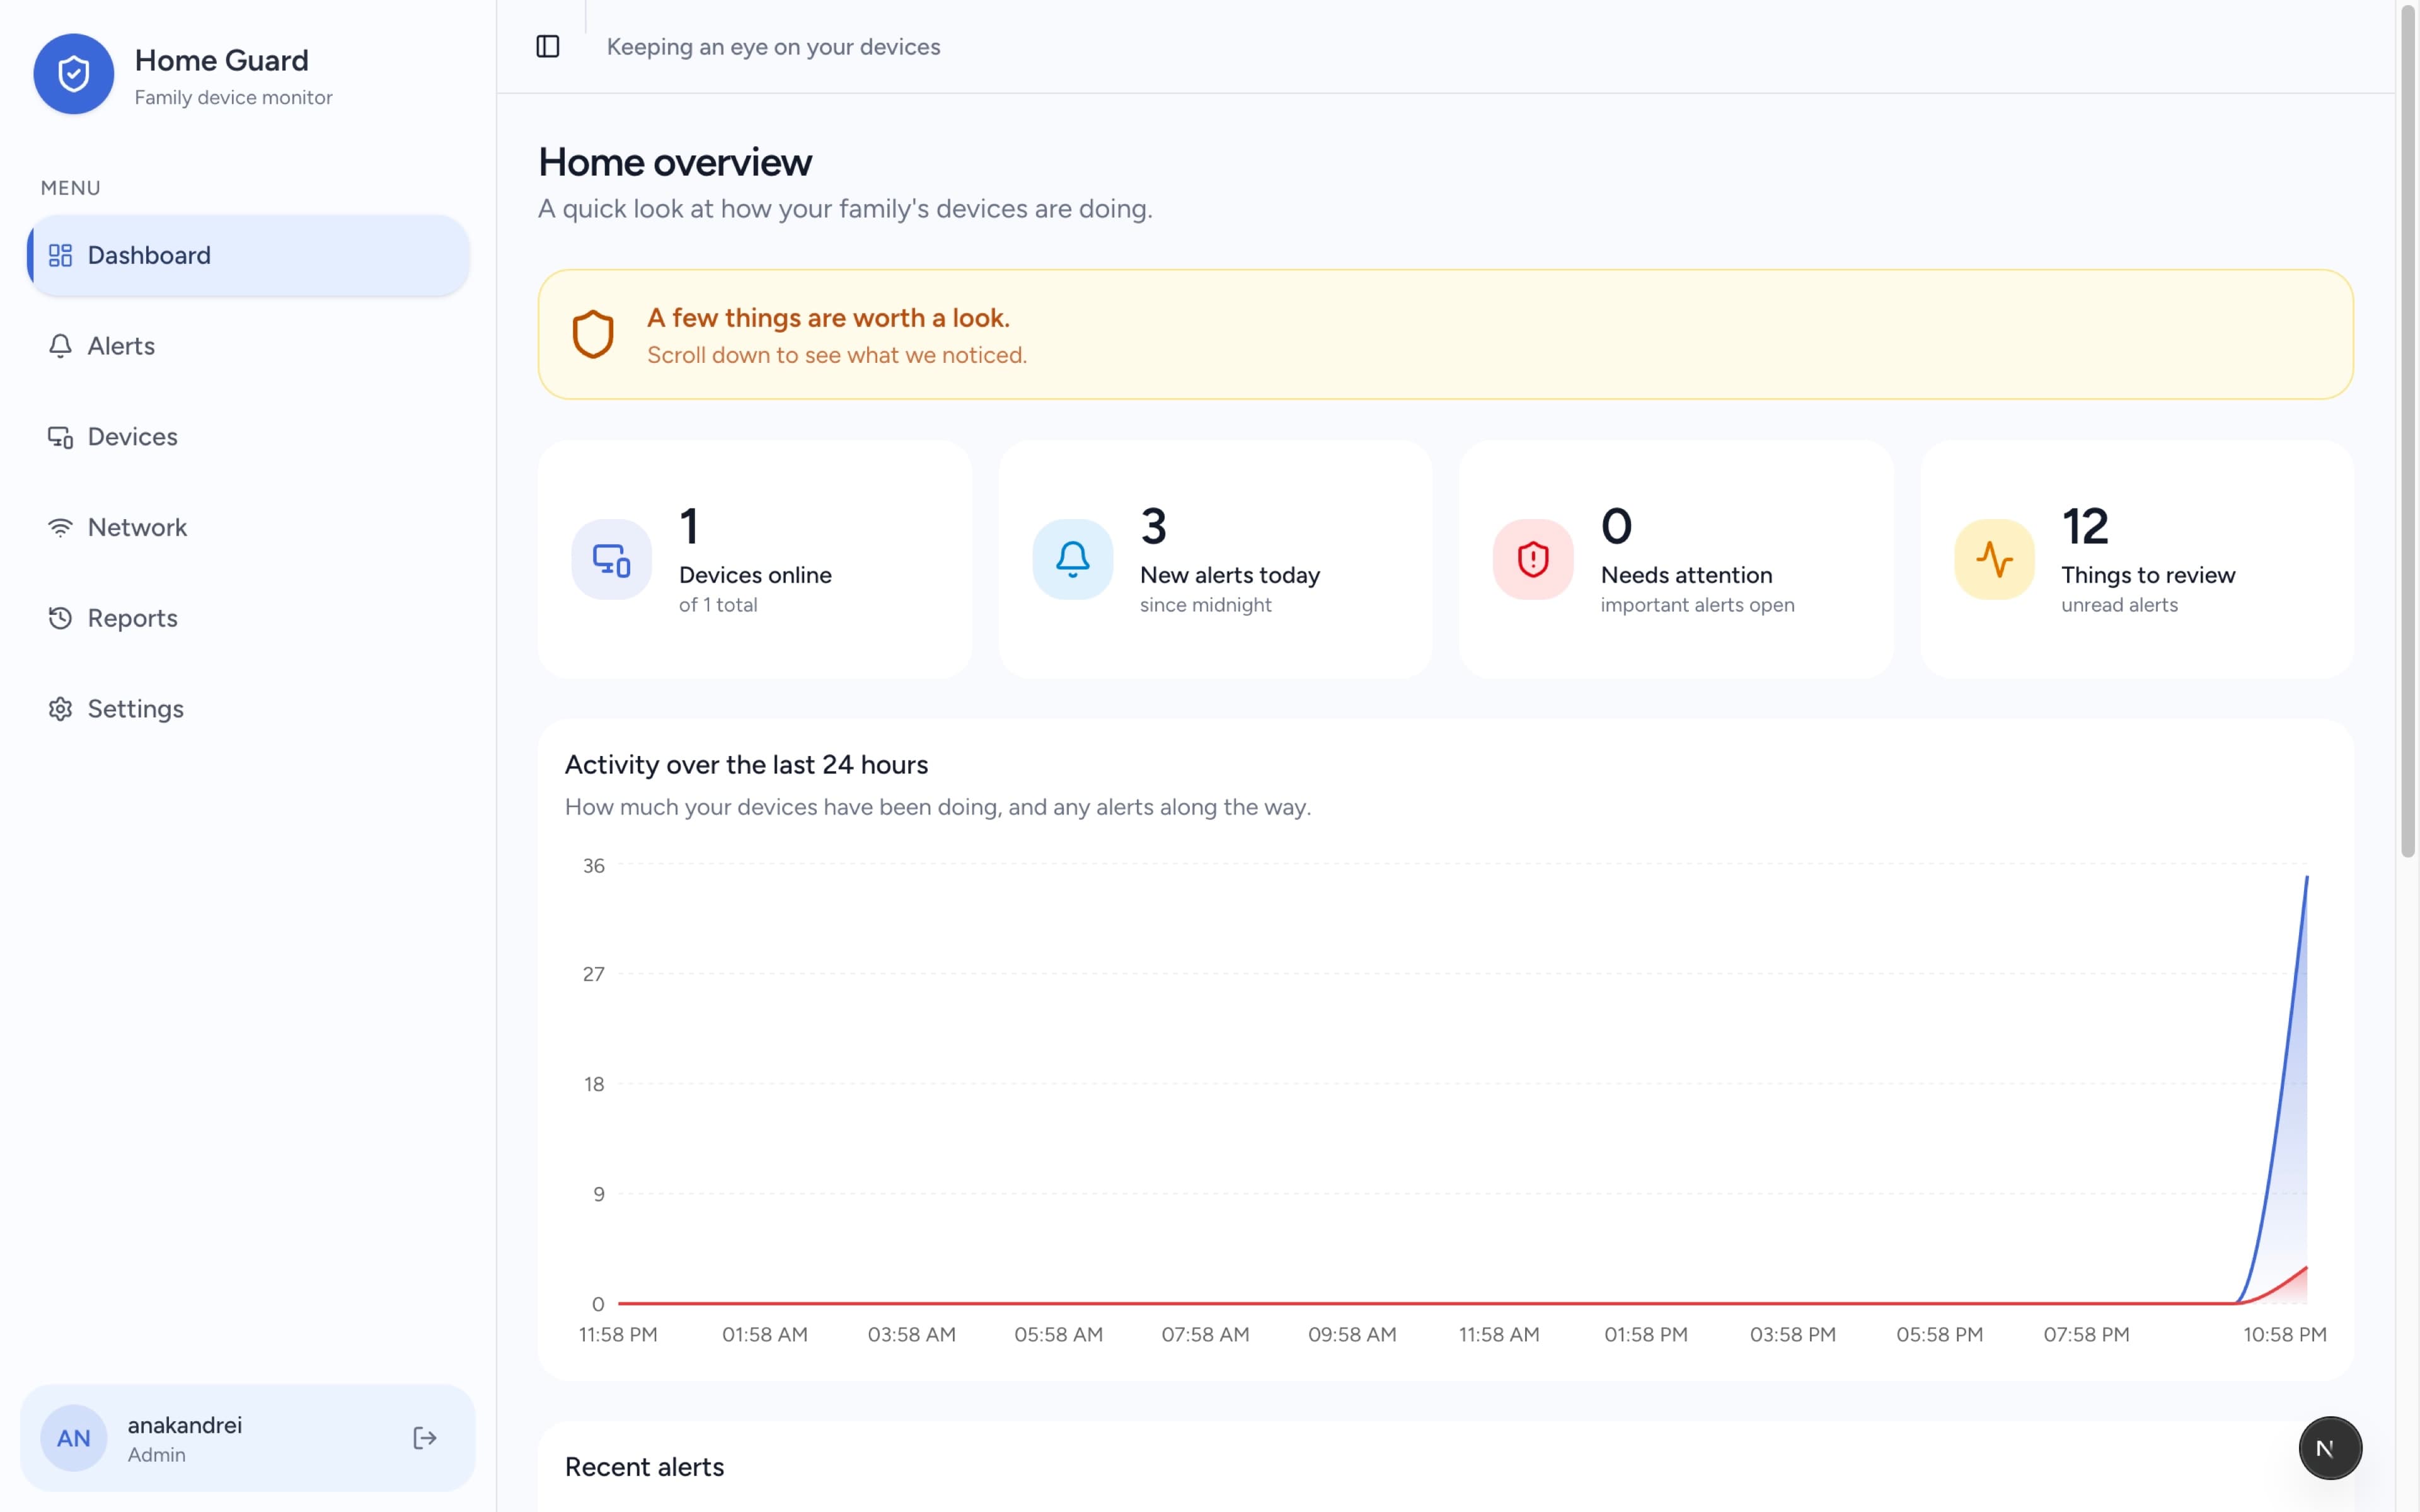
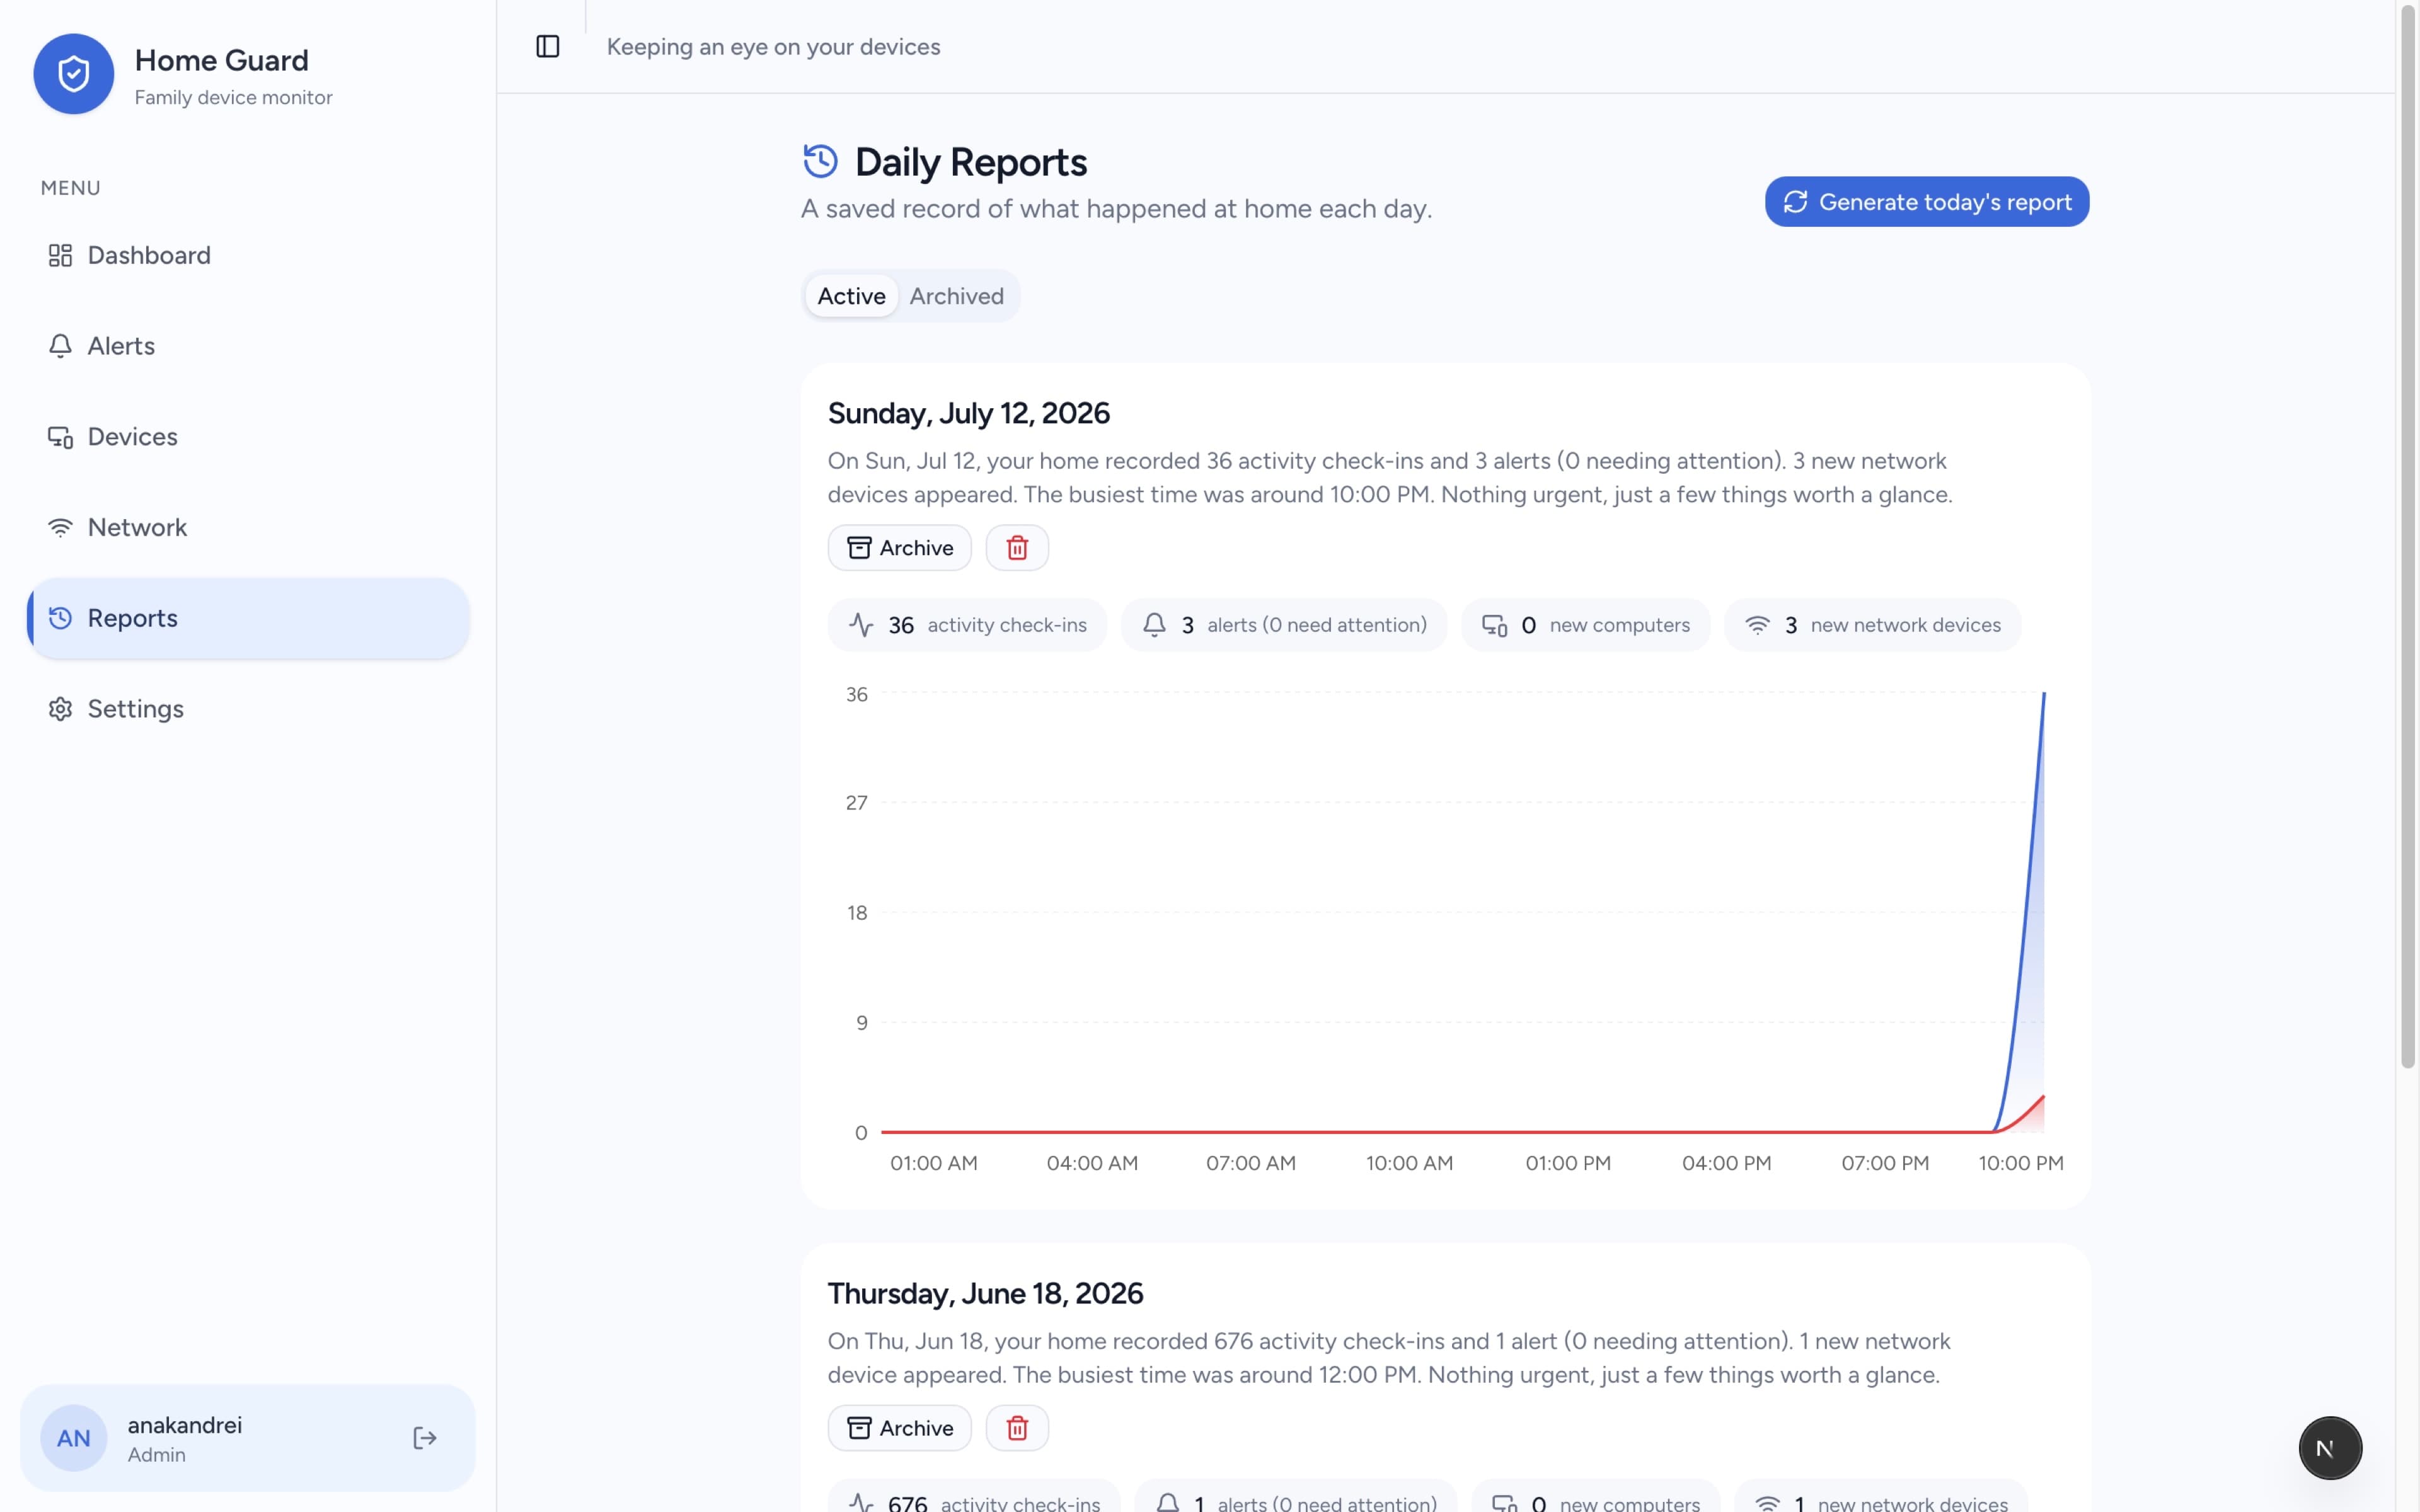
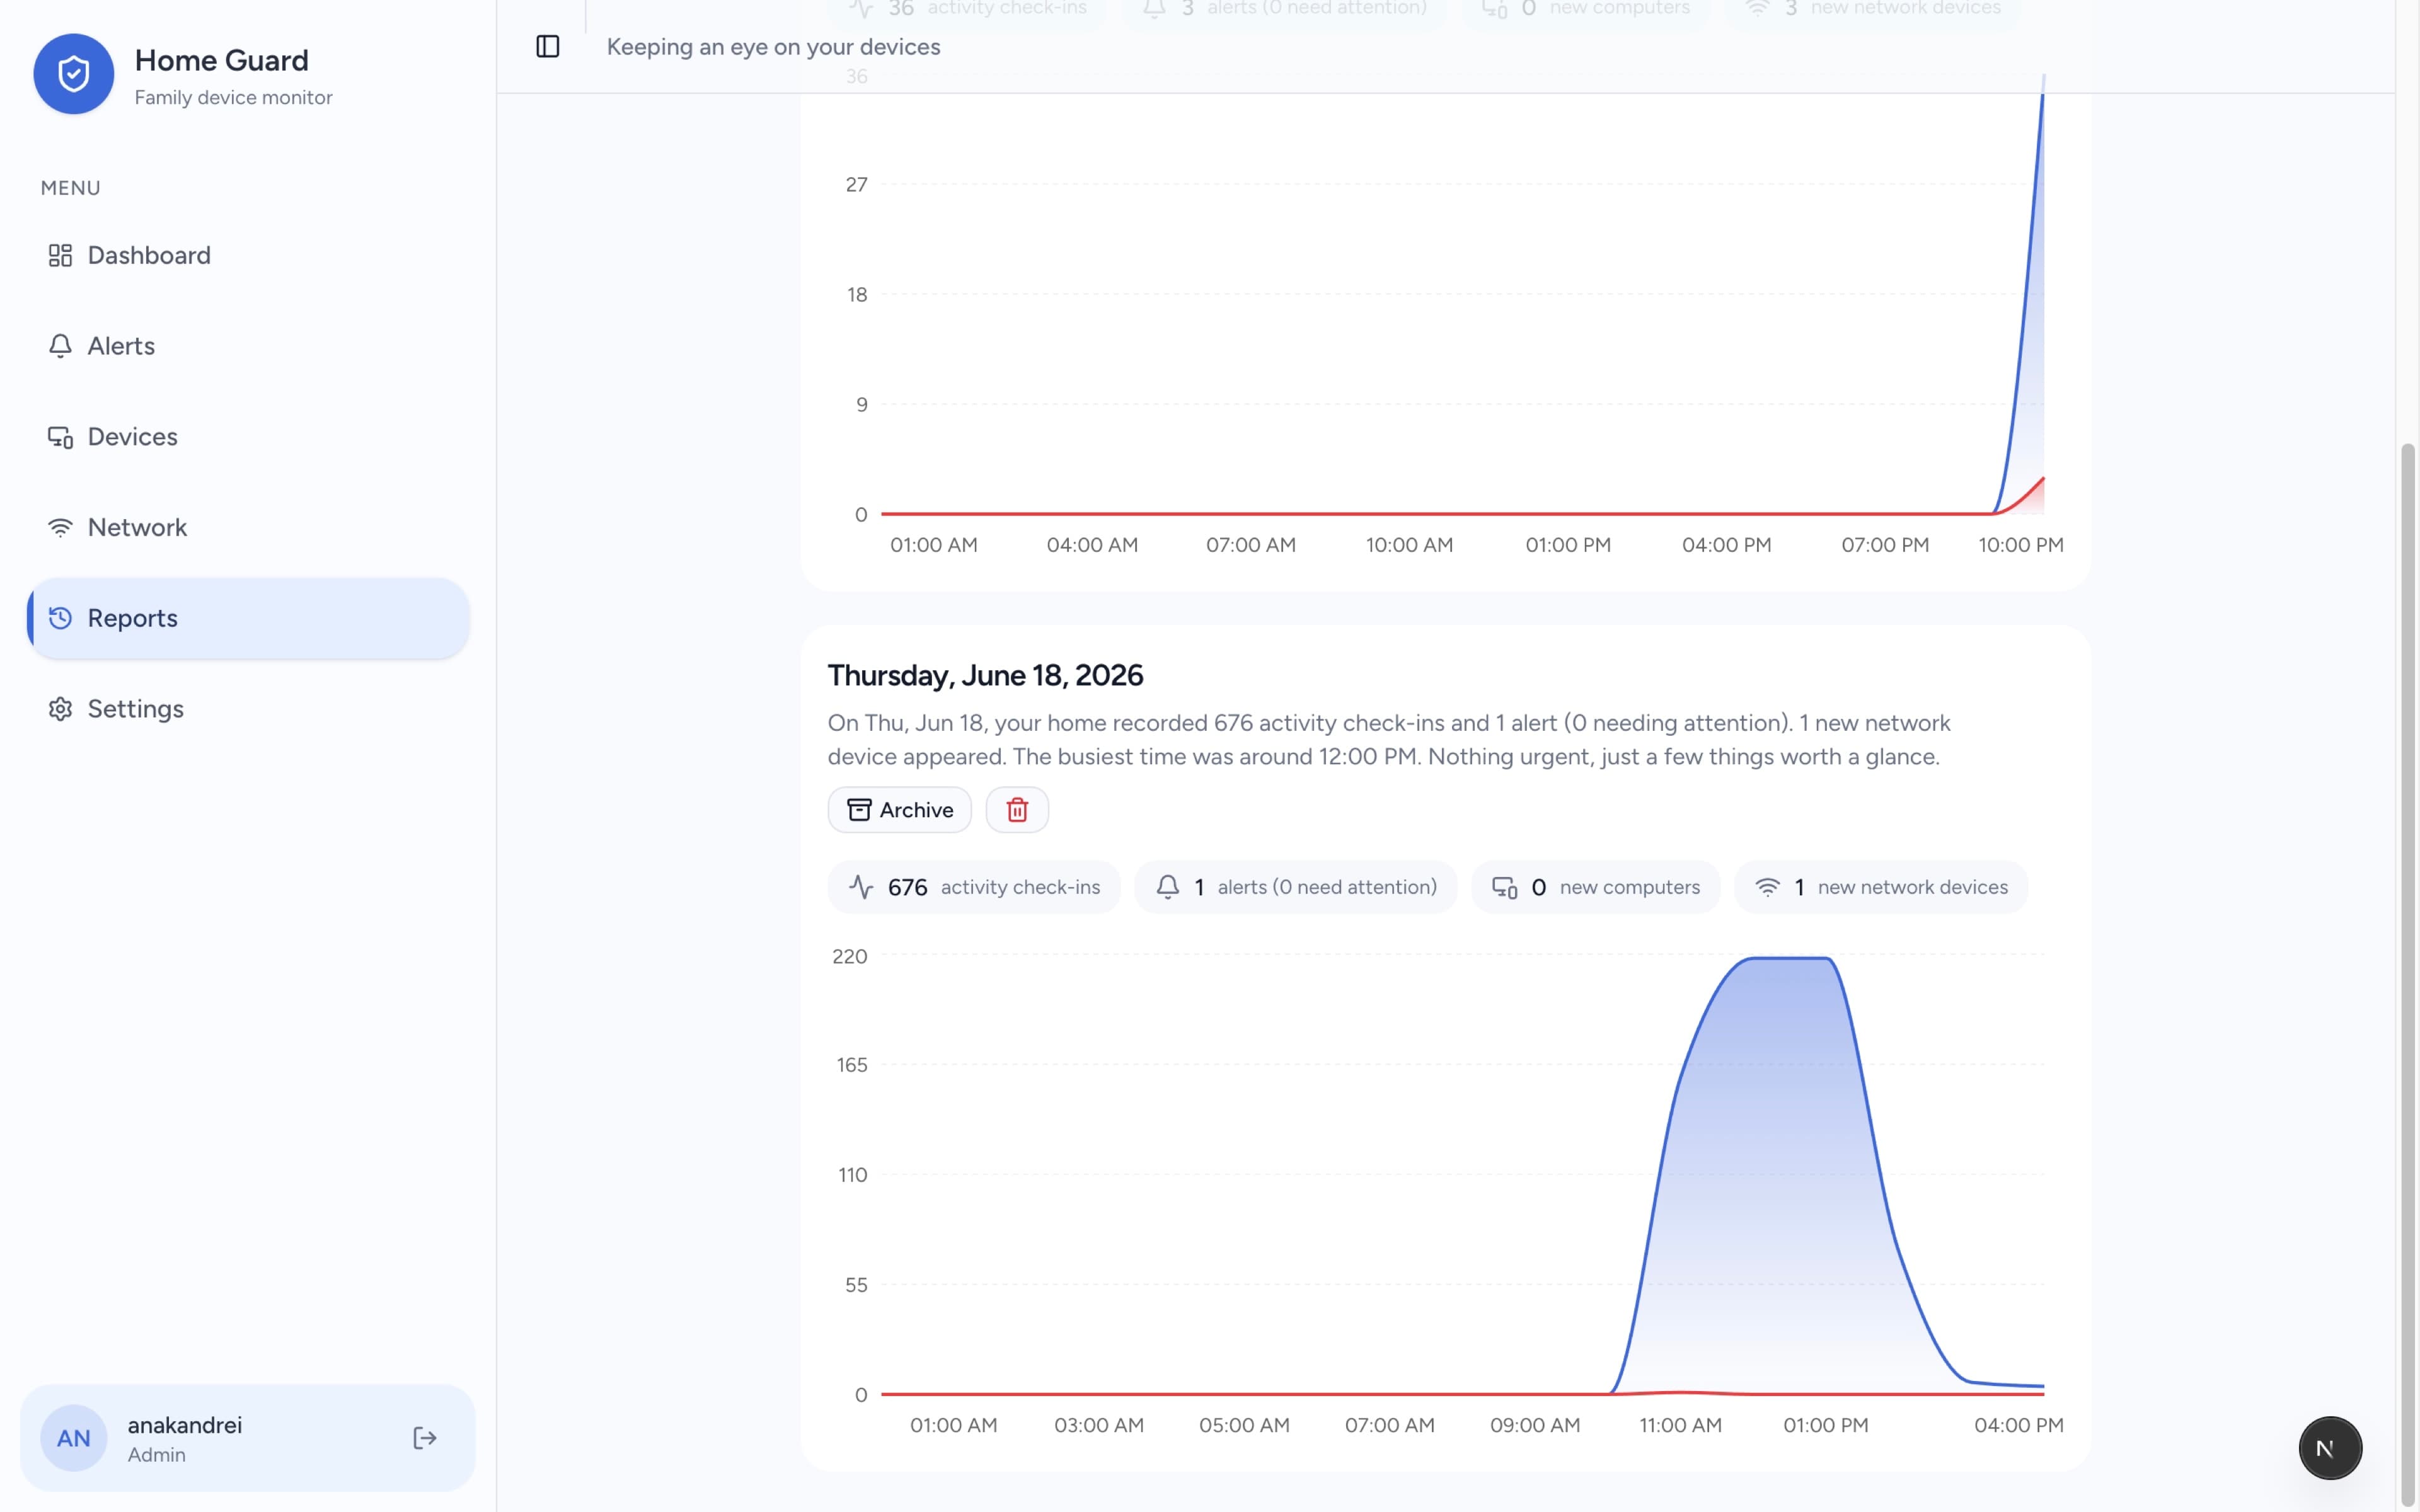
An Endpoint Detection & Response system for monitoring devices and detecting suspicious activity across our home network.
A lightweight agent runs on each computer and reports real telemetry: CPU load, running programs, who is signed in, and network connections. A backend checks every snapshot against a rule-based detection engine that flags known attacker tools, unusually high CPU use, unusual network activity and sudden spikes in running programs.
Findings appear on a shared dashboard as plain-language alerts, such as “Suspicious program is running”, so anyone in the family can understand them without security knowledge. A separate network scanner also lists every other device on the WiFi, including phones and TVs, with nothing installed on them.
Security was a design priority: no secrets are hardcoded, agents authenticate with hashed device credentials, and dashboard logins use JWT with admin and viewer roles.
- Python
- NestJS
- Prisma
- PostgreSQL
- Next.js
- Docker